Azure Cloud Architecture Design
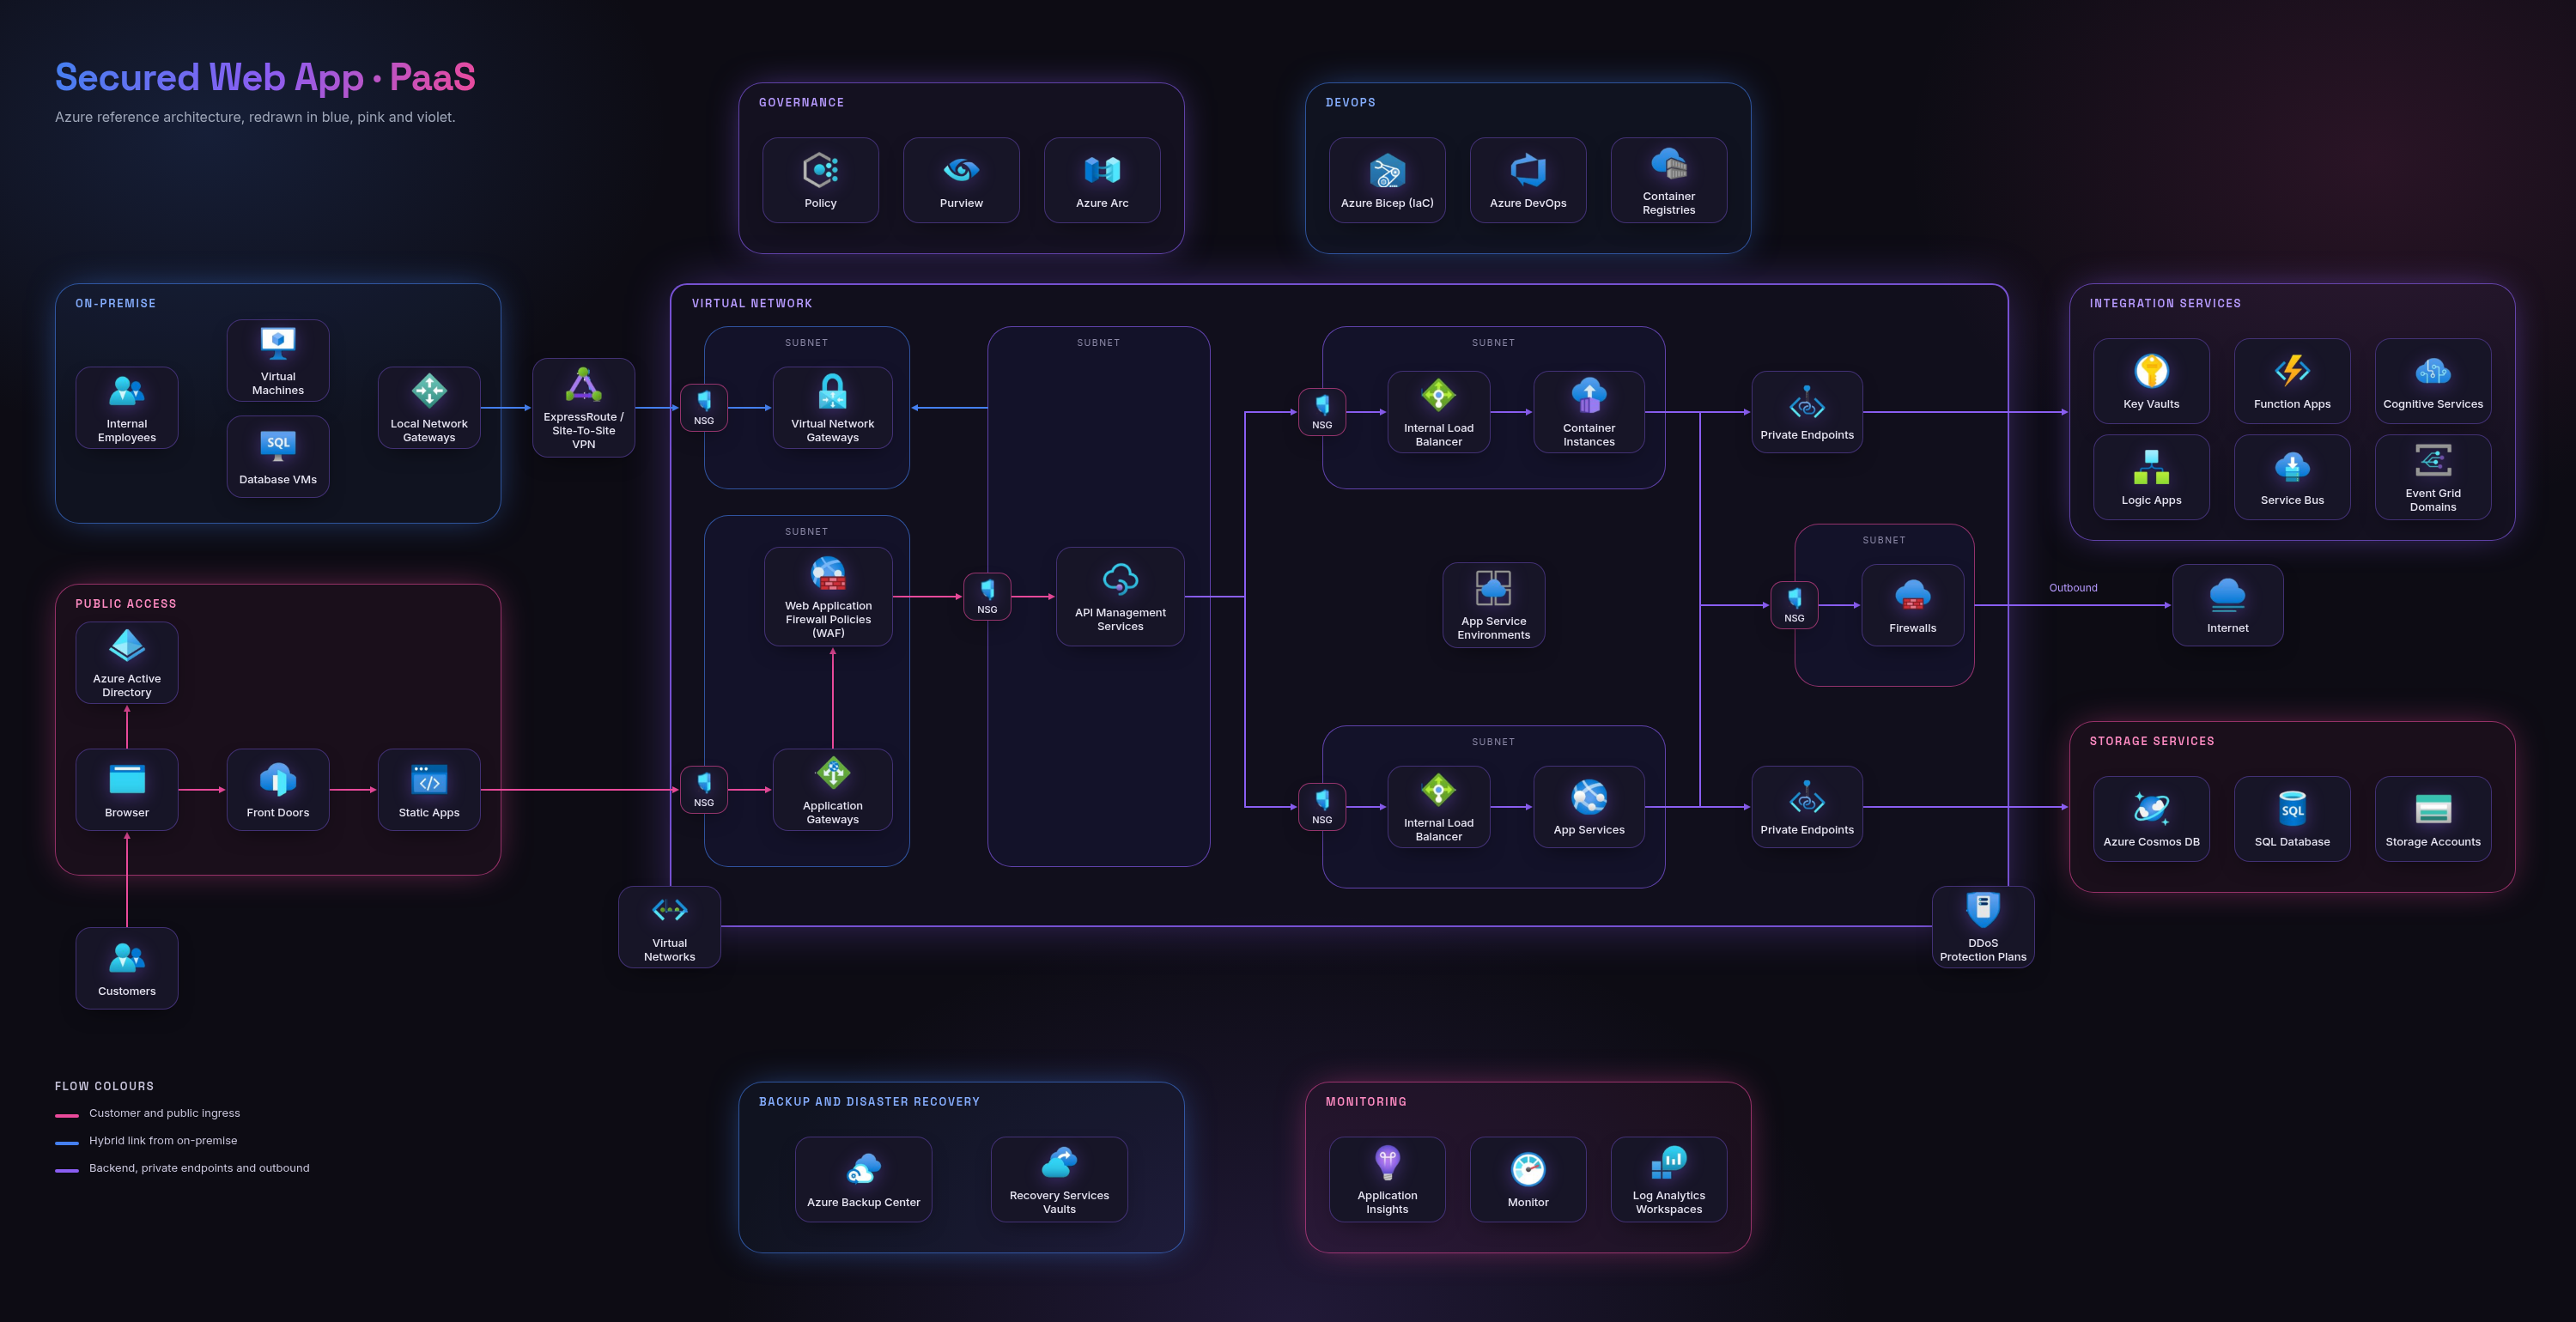
A secured PaaS web app on Azure, with private networking and hybrid access to on-premise.
5 agencies served, with security and performance built in.
Architecture diagram · zoom, drag or double-tap to explore
100%
Follow the data · tap a step
Problem
A public sector web app had to serve customers over the internet and staff from on-premise, without exposing the services and data behind it.
Approach
- Customers reach Static Apps through Front Door, then an Application Gateway with WAF policies; Azure AD handles sign-in.
- Staff connect from on-premise over ExpressRoute or site-to-site VPN into a Virtual Network Gateway.
- API Management routes traffic to App Services and Container Instances behind internal load balancers, with an NSG on every subnet.
- Key Vaults, Function Apps, Logic Apps, Service Bus, Event Grid, Cosmos DB, SQL Database and Storage are reached only through private endpoints; outbound traffic leaves through Azure Firewall.
- Governed with Policy, Purview and Azure Arc; deployed with Bicep and Azure DevOps; backed up with Backup Center and Recovery Services Vaults; monitored with Application Insights, Monitor and Log Analytics.
Results
- One reference architecture covering public access, hybrid connectivity, private backends, governance, DevOps, backup and monitoring.
- DDoS protection on the virtual network.
Industry
Public Sector
Tech stack
AzureFront DoorApplication Gateway (WAF)API ManagementApp ServiceAzure ADBicepAzure DevOps